Sitehop Opens US Office At Defence And Security Hub
September 24, 2026 | Defence, Security, USA
Sitehop, the UK-based post-quantum cybersecurity specialist, has opened a US office in Virginia, Arlington, close to the nation’s military and industrial establishment.
The move is being spearheaded by co-founder and CEO Melissa Chambers, a Mississippi-born former NASA engineer and entrepreneur, the daughter of a USAF electrician.
It comes after Sitehop’s encryption hardware was installed at key sites in Silicon Valley, close to hyperscalers, and Northern Virginia, a hub for the US defence and security sector.
Sitehop has joined Virtus Innovation Center in National Landing, near to the Pentagon and surrounded by defence, government, technology, academic and investment institutions.
Virtus brings together organisations across that community, with connections to groups including hyperscaler AWS, venture capital network VC in DC, university Virginia Tech, strategic investor IQT, Defense Advanced Research Projects Agency (DARPA), geopolitics consultancy WestExec Advisors and the wider National Innovation Quarter ecosystem.
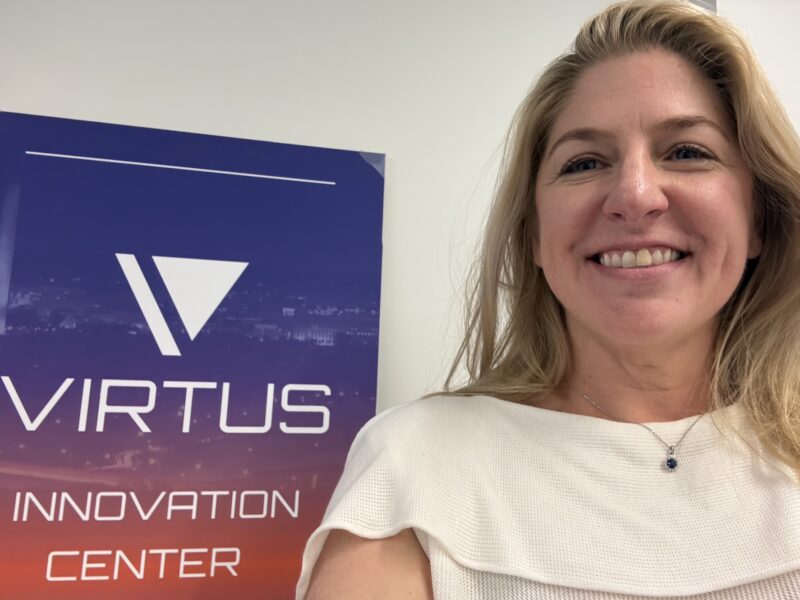 Melissa has been an active presence at industry events since relocating, including Deep Tech Week’s DC Startup Crawl and the 17th Annual Billington CyberSecurity Summit in Washington DC.
She said: “We’ve proved that we can build relationships, win customers and deploy technology in the US from across the Atlantic. Being on the ground means we can do it faster, build deeper relationships and be closer to the people and programmes we want to support.”
Co-founder and CTO Ben Harper, who built his career in defence and intelligence technology at a leading defence prime contractor, added: “We have spent the last few years proving our hardware encryption and high performance post quantum cryptography in demanding telecom and high assurance environments. Now we are building a real presence in the US as we increase our focus on defence, national security and critical infrastructure.”
The company’s sovereign technology takes a different approach to incumbent software-defined wide area network (SD-WAN) products that have become embedded across defence and enterprise networks and is built on reprogrammable hardware rather than a software stack.
Sitehop’s track record includes deployment with a tier-one global telecommunications provider across seven countries, development of the world’s smallest post-quantum encryption device to protect operational technology networks and becoming the first external company admitted to BT’s flagship test facility at Adastral Park, one of the most advanced telecoms testing grounds in Europe.
Notes to Editors:
Sitehop delivers the world’s fastest hardware-enforced, quantum-resistant encryption. As cybersecurity evolves with AI and quantum threats, traditional encryption is struggling to keep pace. Sitehop’s FPGA-powered, crypto-agile solutions deliver unmatched sub-microsecond latency, securing data instantly and proactively so networks stay protected before threats appear.
The World Economic Forum selected Sitehop for its 2026 Technology Pioneers community, bringing together 100 of the world’s most promising early-stage companies with the potential to reshape industries and address global challenges.
For more information, please visit www.sitehop.com
Why Resilience Has Become Retail’s Most Important Cyber Security Strategy
September 22, 2026 | Resilience, Retail, Transformation
For a long time, retail cyber security was built around a single idea: keep the attackers out. Build a strong perimeter, patch the gaps, and hope the walls hold. That idea is no longer enough. The retailers pulling ahead have accepted an uncomfortable truth and built their strategy around it. Sooner or later, something gets through, and what matters most is what happens next.
Retail cyber security can no longer assume the walls will hold
The attack surface has exploded. Payment data now moves through POS terminals, self-checkout, kiosks, ATMs, e-commerce sites, mobile apps and a web of third-party links. Every one of those is a potential way in. At the same time, attackers have become faster, better organised and more focused on disruption than ever.
The made the point plainly. These were not small, obscure businesses. They were large, well-resourced brands with security teams, and they were still knocked offline for weeks. Prevention still matters, but prevention on its own is a losing bet.
From prevention to resilience
Resilience is the shift from stopping every attack to surviving the ones that land. A resilient retailer assumes a breach will happen and designs so that a single compromise stays small, contained and survivable, rather than spreading into a business-wide crisis.
Prevention asks how we keep attackers out. Resilience asks how we keep trading when they get in.
That change in mindset is why resilience now sits at the centre of serious retail cyber security strategies, rather than off to the side as a disaster-recovery afterthought.
What resilience looks like in practice
Resilience is not one tool. It is a set of design choices that work together:
- Containment: segmenting the network so an intruder who reaches one area cannot roam freely into payment systems and beyond.
- Encryption: protecting payment data in motion, so that even intercepted traffic is useless to an attacker.
- Continuity: keeping critical systems trading, or recovering them quickly, when something goes wrong.
- Central control: managing policy, keys and configuration across every store from one place, so you can respond fast and consistently.
Done well, these choices limit the blast radius of any single incident. The goal is simple to state: one compromised device, store or link should never be able to bring down the whole business.
Customer data protection is part of resilience
Resilience and customer data protection are two sides of the same coin. Much of what a retailer holds, from cardholder data to loyalty and account details, is exactly what attackers are after. Strong customer data protection, built on encryption and tight control over who and what can reach sensitive information, both reduces the chance of a damaging breach and limits the harm when one occurs.
It also protects something harder to rebuild than any system: customer trust. Effective customer data protection keeps a bad day from becoming a lasting reputational wound, and cardholder data protection in particular sits at the heart of meeting PCI DSS 4.0 objectives.
Preparing for what comes next
A resilient strategy also looks forward. Cryptography itself is changing, with post-quantum computing on the horizon and encrypted data captured today at risk of being broken later. Building on crypto-agile foundations, able to adopt new standards without replacing every device, is how retailers stay resilient against tomorrow’s threats as well as today’s.
Resilience is the strategy
Retail cyber security is no longer about building a taller wall. It is about designing a business that keeps running, keeps protecting its customers and keeps earning trust, even under attack. Resilience is what ties payments, data protection and continuity into one coherent strategy.
Sitehop helps retailers build that resilience: end-to-end encryption for payment data, protection for data in motion, and crypto-agile, PQC-ready security that spans every store and network without slowing operations. To see how it works in the field, read how SAFEcore Edge secures data from the field to HQ.
Build retail cyber security that bends without breaking.
Book a Sitehop demo to see how resilient encryption protects payments and customer data across your estate.
Sitehop. Engineered for speed. Built for the future.
Why Software Encryption Can’t Keep Up With Contested, Connected Missions
September 17, 2026 | Defence, Encryption
Every mission depends on trust before it depends on speed.
The data starts moving long before people or platforms do, across the contested edge, through legacy systems built decades ago, into the hands of allies running entirely different systems. Whether that connectivity is happening isn’t the question. It already is. Whether it’s controlled, is.
The edge doesn’t wait for connectivity, and neither can the mission
Mission environments are shifting toward disconnected, compute-at-the-edge operations, a trend accelerated by lessons from recent conflicts. Distributed compute, often running on disposable, person-portable platforms, needs sub-second latency under jamming and drone-swarm conditions. That’s a demanding bar before security enters the picture at all. Add post-quantum cryptography’s packet overhead on top of a software stack that was never built for it, and the result is exactly the wrong trade-off: security that costs the mission it’s meant to protect.
This is where general-purpose software encryption runs out of road. It adds latency and becomes a bottleneck under load. It carries a large, complex attack surface that’s hard to secure and harder to audit. It wasn’t built for denial or intermittent connectivity: the default condition at the tactical edge, not the exception. And critically, it can’t be upgraded to post-quantum cryptography without a forklift replacement of the infrastructure running it.
Deterministic, not just fast
Security has traditionally meant a trade-off: stronger encryption for more latency, lower throughput, or changed application behaviour. In defence, that trade-off isn’t acceptable.
Whether protecting a radar system, a command network or an autonomous platform, operators need confidence that stronger security won’t alter timing, packet flow or system performance. That’s a different bar than “fast.” It’s deterministic performance: security that’s effectively invisible to the application, so the network behaves exactly as it always has, only with stronger protection wrapped around every packet.
Why the hardware boundary matters
Hardware-enforced Layer 3 IPsec runs at line rate with sub-millisecond latency, across any complex Layer 3 network: internet, MPLS, 5G/LTE, satellite or Starlink. Rather than routing sensitive traffic through multiple software layers, cryptographic operations are isolated inside dedicated hardware, while management and configuration functions stay separate from customer data. That separation gives security teams something software architectures rarely can: certainty about exactly where encryption happens, what protects it, and where the cryptographic boundary sits: a boundary that can be audited, not just asserted.
The crypto agility that matters here isn’t a marketing term either. The same physical appliance can move from classical algorithms, through a hybrid state, to fully post-quantum algorithms as standards mature, without replacing infrastructure or needing an engineer at the edge to do it.
Interoperable with the network you already have
None of this requires a flat, single-vendor architecture. Segmentation capabilities proven at commercial telecom scale (isolating millions of customers across multinational networks) translate directly into isolating users, systems and operational domains within defence and coalition environments. Instead of a compromise spreading laterally across a flat network, it’s contained to the segment it started in. That interoperability across coalition partners, legacy platforms and mixed Layer 3 networks is what lets hardware-enforced security sit underneath an existing estate rather than requiring a new one.
That difference compounds under contested conditions. Operators keep secure reach-back and a trustworthy operating picture even when conditions are jammed, denied or intermittent, because the security layer was built for those conditions from the start, not adapted to tolerate them.
The comparison that matters to an evaluator
| Software VPNs & firewalls | Hardware-enforced conduit | |
| Performance under load | Adds latency, becomes a bottleneck | Line-rate, sub-millisecond |
| Attack surface | Large, complex software stack | Purpose-built hardware, minimal surface |
| Denied/intermittent conditions | Not built for it | Designed for it |
| Data / management plane | Mixed together in one software stack | Physically separated, auditable boundary |
| Post-quantum readiness | Can’t be upgraded without replacement | Crypto-agile, no infrastructure swap |
| Integrity | Vulnerable to credential theft, residential proxies | Tamper-proof, attested, secure boot |
The mission moves at the speed of trust
Software encryption was never built to keep pace with a contested, connected battlespace, and retrofitting it after the fact costs more than building on hardware designed for exactly this problem from day one.
See how this plays out across coalition networks, legacy platforms and the supply chain that feeds them: download the PQC Migration Readiness Guide, or Book a Sitehop demo to see how end-to-end encryption keeps data safe.
Or call us: +44 (0)114 478 2366
Sitehop. Engineered for resilience. Built for the life.
About Us
Sitehop provides faster, better, greener alternatives to the encryption options on the market today.