Sitehop Opens US Office At Defence And Security Hub
September 24, 2026 | Defence, Security, USA
Sitehop, the UK-based post-quantum cybersecurity specialist, has opened a US office in Virginia, Arlington, close to the nation’s military and industrial establishment.
The move is being spearheaded by co-founder and CEO Melissa Chambers, a Mississippi-born former NASA engineer and entrepreneur, the daughter of a USAF electrician.
It comes after Sitehop’s encryption hardware was installed at key sites in Silicon Valley, close to hyperscalers, and Northern Virginia, a hub for the US defence and security sector.
Sitehop has joined Virtus Innovation Center in National Landing, near to the Pentagon and surrounded by defence, government, technology, academic and investment institutions.
Virtus brings together organisations across that community, with connections to groups including hyperscaler AWS, venture capital network VC in DC, university Virginia Tech, strategic investor IQT, Defense Advanced Research Projects Agency (DARPA), geopolitics consultancy WestExec Advisors and the wider National Innovation Quarter ecosystem.
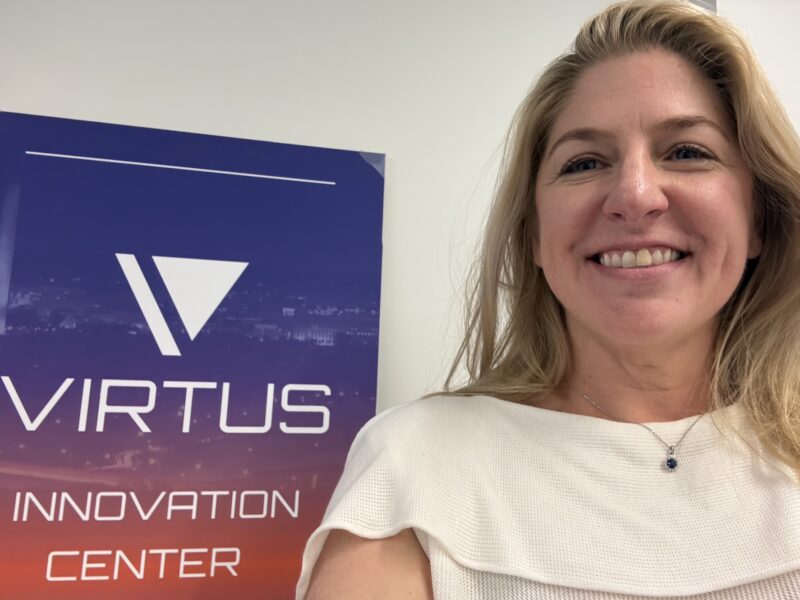 Melissa has been an active presence at industry events since relocating, including Deep Tech Week’s DC Startup Crawl and the 17th Annual Billington CyberSecurity Summit in Washington DC.
She said: “We’ve proved that we can build relationships, win customers and deploy technology in the US from across the Atlantic. Being on the ground means we can do it faster, build deeper relationships and be closer to the people and programmes we want to support.”
Co-founder and CTO Ben Harper, who built his career in defence and intelligence technology at a leading defence prime contractor, added: “We have spent the last few years proving our hardware encryption and high performance post quantum cryptography in demanding telecom and high assurance environments. Now we are building a real presence in the US as we increase our focus on defence, national security and critical infrastructure.”
The company’s sovereign technology takes a different approach to incumbent software-defined wide area network (SD-WAN) products that have become embedded across defence and enterprise networks and is built on reprogrammable hardware rather than a software stack.
Sitehop’s track record includes deployment with a tier-one global telecommunications provider across seven countries, development of the world’s smallest post-quantum encryption device to protect operational technology networks and becoming the first external company admitted to BT’s flagship test facility at Adastral Park, one of the most advanced telecoms testing grounds in Europe.
Notes to Editors:
Sitehop delivers the world’s fastest hardware-enforced, quantum-resistant encryption. As cybersecurity evolves with AI and quantum threats, traditional encryption is struggling to keep pace. Sitehop’s FPGA-powered, crypto-agile solutions deliver unmatched sub-microsecond latency, securing data instantly and proactively so networks stay protected before threats appear.
The World Economic Forum selected Sitehop for its 2026 Technology Pioneers community, bringing together 100 of the world’s most promising early-stage companies with the potential to reshape industries and address global challenges.
For more information, please visit www.sitehop.com
Why Software Encryption Can’t Keep Up With Contested, Connected Missions
September 17, 2026 | Defence, Encryption
Every mission depends on trust before it depends on speed.
The data starts moving long before people or platforms do, across the contested edge, through legacy systems built decades ago, into the hands of allies running entirely different systems. Whether that connectivity is happening isn’t the question. It already is. Whether it’s controlled, is.
The edge doesn’t wait for connectivity, and neither can the mission
Mission environments are shifting toward disconnected, compute-at-the-edge operations, a trend accelerated by lessons from recent conflicts. Distributed compute, often running on disposable, person-portable platforms, needs sub-second latency under jamming and drone-swarm conditions. That’s a demanding bar before security enters the picture at all. Add post-quantum cryptography’s packet overhead on top of a software stack that was never built for it, and the result is exactly the wrong trade-off: security that costs the mission it’s meant to protect.
This is where general-purpose software encryption runs out of road. It adds latency and becomes a bottleneck under load. It carries a large, complex attack surface that’s hard to secure and harder to audit. It wasn’t built for denial or intermittent connectivity: the default condition at the tactical edge, not the exception. And critically, it can’t be upgraded to post-quantum cryptography without a forklift replacement of the infrastructure running it.
Deterministic, not just fast
Security has traditionally meant a trade-off: stronger encryption for more latency, lower throughput, or changed application behaviour. In defence, that trade-off isn’t acceptable.
Whether protecting a radar system, a command network or an autonomous platform, operators need confidence that stronger security won’t alter timing, packet flow or system performance. That’s a different bar than “fast.” It’s deterministic performance: security that’s effectively invisible to the application, so the network behaves exactly as it always has, only with stronger protection wrapped around every packet.
Why the hardware boundary matters
Hardware-enforced Layer 3 IPsec runs at line rate with sub-millisecond latency, across any complex Layer 3 network: internet, MPLS, 5G/LTE, satellite or Starlink. Rather than routing sensitive traffic through multiple software layers, cryptographic operations are isolated inside dedicated hardware, while management and configuration functions stay separate from customer data. That separation gives security teams something software architectures rarely can: certainty about exactly where encryption happens, what protects it, and where the cryptographic boundary sits: a boundary that can be audited, not just asserted.
The crypto agility that matters here isn’t a marketing term either. The same physical appliance can move from classical algorithms, through a hybrid state, to fully post-quantum algorithms as standards mature, without replacing infrastructure or needing an engineer at the edge to do it.
Interoperable with the network you already have
None of this requires a flat, single-vendor architecture. Segmentation capabilities proven at commercial telecom scale (isolating millions of customers across multinational networks) translate directly into isolating users, systems and operational domains within defence and coalition environments. Instead of a compromise spreading laterally across a flat network, it’s contained to the segment it started in. That interoperability across coalition partners, legacy platforms and mixed Layer 3 networks is what lets hardware-enforced security sit underneath an existing estate rather than requiring a new one.
That difference compounds under contested conditions. Operators keep secure reach-back and a trustworthy operating picture even when conditions are jammed, denied or intermittent, because the security layer was built for those conditions from the start, not adapted to tolerate them.
The comparison that matters to an evaluator
| Software VPNs & firewalls | Hardware-enforced conduit | |
| Performance under load | Adds latency, becomes a bottleneck | Line-rate, sub-millisecond |
| Attack surface | Large, complex software stack | Purpose-built hardware, minimal surface |
| Denied/intermittent conditions | Not built for it | Designed for it |
| Data / management plane | Mixed together in one software stack | Physically separated, auditable boundary |
| Post-quantum readiness | Can’t be upgraded without replacement | Crypto-agile, no infrastructure swap |
| Integrity | Vulnerable to credential theft, residential proxies | Tamper-proof, attested, secure boot |
The mission moves at the speed of trust
Software encryption was never built to keep pace with a contested, connected battlespace, and retrofitting it after the fact costs more than building on hardware designed for exactly this problem from day one.
See how this plays out across coalition networks, legacy platforms and the supply chain that feeds them: download the PQC Migration Readiness Guide, or Book a Sitehop demo to see how end-to-end encryption keeps data safe.
Or call us: +44 (0)114 478 2366
Sitehop. Engineered for resilience. Built for the life.
Before the Mission Advances, the Data Moves
August 13, 2026 | Defence, Encryption, Resilience
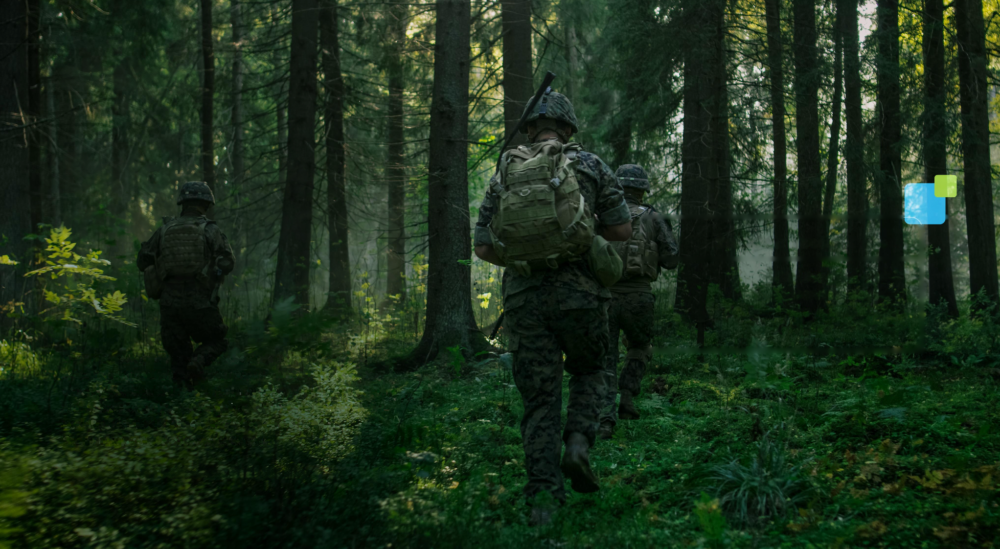
A modern military mission doesn’t begin when troops deploy, a ship leaves port or an aircraft takes off.
It begins when data starts moving.
Mission plans, intelligence, sensor feeds, logistics, communications and command decisions all travel across networks long before people or platforms move into position. If that data is delayed, exposed or compromised, the mission is already at risk.
For decades, defence organisations have invested heavily in protecting physical assets. Yet many of the networks connecting those assets still rely on infrastructure designed years, sometimes decades, ago. Replacing those systems isn’t practical and, in many cases, isn’t even possible.
The challenge facing defence today is no longer simply how to build the next generation of secure networks. It is how to secure the networks already carrying today’s missions.
Legacy isn’t the problem. Leaving it exposed is.
Defence has always been different from the commercial world.
Platforms remain operational for decades. Radar systems, communications equipment, naval platforms, vehicles and industrial control systems frequently outlive several generations of IT. They continue performing critical roles long after the software around them has evolved. Replacing those systems simply because cryptography has changed isn’t financially or operationally realistic.
Instead, organisations face a far more pressing question: how do you protect long-life assets without redesigning everything around them?
And just because legacy platforms can stay in place doesn’t mean the threat is standing still with them. Modern warfare is evolving quickly: contested and denied spectrum, autonomous systems, and adversaries who go after the weakest link in a network rather than the newest one. Protecting what’s already in the field is only half the challenge. Defence also needs new, innovative approaches, delivered by companies built to move at the pace the threat now demands, not the multi-year timelines legacy suppliers were designed around.
As post-quantum cryptography (PQC) becomes a national priority, many are beginning to recognise that the answer lies in securing what already exists, rather than replacing it. One increasingly attractive approach is to create a cryptographic overlay around legacy equipment, surrounding trusted systems with modern protection while leaving proven operational behaviour untouched. Applications continue working exactly as before; only the security surrounding them changes. That emerging approach formed a central theme of our recent defence strategy discussion.
Performance is operational assurance
Security has traditionally been viewed as a compromise. Stronger encryption often meant more latency, lower throughput or changes to application behaviour.
In defence, those compromises simply aren’t acceptable.
Whether protecting a radar system, command network or autonomous platform, operators need confidence that introducing stronger security will not alter timing, packet flow or system performance.
The goal isn’t simply faster encryption. It’s deterministic performance, where security becomes effectively invisible to the application. Networks behave exactly as they always have, only with stronger protection around every packet.
When engineers can introduce modern cryptography without changing how systems communicate, upgrading security becomes significantly less disruptive.
Why hardware matters
Most modern security platforms rely heavily on software, delivering flexibility but also increasing complexity. Every operating system, software library and management layer expands the potential attack surface.
Hardware-enforced security takes a fundamentally different approach.
Rather than processing sensitive traffic through multiple software layers, cryptographic operations are isolated inside dedicated hardware, while management functions remain separate from customer data. The result is a smaller attack surface, clearly defined cryptographic boundaries and an architecture that is easier to audit and trust. During our discussion, this separation between management, configuration and data planes emerged as one of the key differentiators for high-assurance environments.
For defence organisations, that physical separation provides something increasingly valuable: certainty. Security teams know exactly where encryption begins, what protects it and where the cryptographic boundary sits.
Commercial innovation is strengthening national security
Some of the most valuable innovation now entering defence has been refined elsewhere.
Global telecommunications providers have spent years solving problems around resilience, availability, segmentation and operating secure networks at enormous scale. Those lessons translate remarkably well into national security environments.
Capabilities originally designed to isolate customers across multinational telecoms networks can also isolate users, systems and operational domains within defence. Instead of flat architectures where compromise can spread laterally, organisations can build segmented environments that reduce blast radius and contain attacks far more effectively.
The technology may have matured in commercial networks, but its operational value is increasingly being recognised in defence.
Modernisation doesn’t always mean replacement
Quantum computing, AI-assisted cyber attacks and increasingly sophisticated nation-state threats are accelerating the need to modernise security. Yet modernisation should not automatically be confused with replacement.
For organisations responsible for defence, government and critical national infrastructure, the most practical path forward is often to retain trusted platforms, preserve operational workflows and simply modernise the protection surrounding them.
That approach avoids costly infrastructure refresh programmes while enabling organisations to strengthen security today rather than waiting years for complete system replacement.
Before the mission moves…
Every mission depends on trust.
Trust that systems behave predictably. Trust that information arrives intact. Trust that communications remain confidential. Long before a vehicle moves, before a sensor reports or before a commander makes a decision, data is already travelling across the network. Protecting that journey is rapidly becoming one of the defining cybersecurity challenges of the next decade. Because in modern defence, the first thing that moves is rarely the mission itself.
It’s the data.
For organisations looking to strengthen security without replacing the infrastructure they depend on, Sitehop’s SAFE Series™ provides a hardware-enforced cryptographic overlay designed for mission-critical networks. Spanning core, edge and centralised management, the platform delivers deterministic, ultra-low-latency encryption, physical network segmentation and post-quantum cryptographic agility, enabling defence, government and critical infrastructure organisations to protect legacy and modern systems alike while preserving the performance and resilience their missions demand.
Read the full PQC Migration Readiness Guide and explore more at sitehop.com
Book a Sitehop demo to see how end-to-end encryption keeps data safe.
Or call us: +44 (0)114 478 2366
Sitehop.
Sitehop. Engineered for resilience. Built for the life.
About Us
Sitehop provides faster, better, greener alternatives to the encryption options on the market today.